Connect your Microsoft Power Platform environment to Capsule Security for complete visibility into your AI agents, workflows, and conversation history across Copilot Studio and Power Automate.

This integration uses Microsoft Entra ID (Azure AD) authentication to sync:
- Agents - Copilots built in Copilot Studio
- Tools - Actions, plugins, Power Automate flows, and connectors
- Knowledge Bases - Data sources and knowledge articles attached to copilots
- Conversations - Chat sessions and conversation history
- Audit - Activity logs with action invocations and session tracking
Before you begin, ensure you have:
- An active Microsoft Power Platform environment with Copilot Studio and/or Power Automate
- An Azure Entra ID account that is System Administrator in each environment Capsule should monitor, with a Power Apps or Dynamics 365 license assigned. Global, Power Platform, and Dynamics 365 admins, with the role assigned directly and not through a group, can grant themselves System Administrator. See Environments Fail with an Application User Error
- Access to the Capsule Security portal
For more information about Power Platform roles, see Administering Power Platform.
Start the integration setup from the Capsule Security portal.
Log in to the Capsule Security portal
Click Integrations in the left sidebar
Find the Microsoft Power Platform card and click Set up Integration
Click Connect with Microsoft
You'll be redirected to Microsoft's sign-in page
Grant Capsule the necessary permissions to access your Power Platform resources.
Sign in with your Microsoft account that has the required permissions (see Prerequisites)
Review the permissions requested by the Capsule application
Click Accept to grant consent
Capsule requests the following permissions across Microsoft APIs. Most grant read-only access used for discovery and monitoring; a few setup permissions (application install, role assignment, and user provisioning) are required to install the Capsule application and maintain ongoing synchronization.
| Permission | Type | Description | Admin consent required | Justification |
|---|---|---|---|---|
| mcp.tools | Delegated | Access Dataverse MCP server tools | No | Not used. Capsule does not call the Dataverse MCP server |
| user_impersonation | Delegated | Access Common Data Service as organization users | No | Query Dataverse for environment data, copilots, flows, and users on behalf of the authorizing user |
| Permission | Type | Description | Admin consent required | Justification |
|---|---|---|---|---|
| AiEnterpriseInteraction.Read.All | Application | Read all AI enterprise interactions | Yes | Ingest enterprise AI interaction records for conversation and activity history |
| AuditLogsQuery.Read.All | Application | Read audit logs data from all services | Yes | Query the Purview unified audit log for Copilot Studio agent interactions, the only source of activity for Microsoft 365 Copilot (Lite) agents |
| Reports.Read.All | Application | Read all usage reports | Yes | Retrieve usage reports for adoption and activity insights |
| User.Read | Delegated | Sign in and read user profile | No | Sign in the authorizing user and read their profile during setup |
| User.Read.All | Application | Read all users' full profiles | Yes | Resolve owners and participants across discovered agents and flows |
| Permission | Type | Description | Admin consent required | Justification |
|---|---|---|---|---|
| Activity.Read.All | Delegated | Allow the application to read activities | No | Read flow run activity for audit and run history |
| Approvals.Read.All | Delegated | Allow the application to read approvals | No | Read approval steps referenced by flows |
| Flows.Read.All | Delegated | Allow the application to read flows | No | Discover and read Power Automate flow definitions |
| Flows.Read.Plans | Delegated | Allow the application read only permission for flow | No | Read flow plan metadata |
| Permission | Type | Description | Admin consent required | Justification |
|---|---|---|---|---|
| CopilotStudio.MinimalBot.ReadWrite | Delegated | Read and write access for MinimalBot | No | Read Copilot Studio Lite agent definitions. The endpoint only accepts this scope, but Capsule never writes to it |
| ResourceQuery.Resources.Read | Delegated | Read Resources | No | Query Power Platform resources during environment discovery |
| UserManagement.Users.Apply | Delegated | Apply user management operations | No | Provision the Capsule application user required for ongoing synchronization |
For more information about the consent experience, see User and admin consent in Azure.
After you grant consent, Capsule automatically configures the integration.
- All Power Platform environments you have access to are discovered
- Copilot Studio bots and Power Automate flows within those environments are detected
- Required access permissions are configured automatically
If Capsule cannot add its application user in an environment, see Environments Fail with an Application User Error.
Some tenants limit who can use Copilot Studio to members of specific Microsoft Entra security groups, through the Copilot Studio authors tenant setting and related settings in the Power Platform admin center. Capsule installs into each environment by creating an application user for the Capsule Entra application and assigning it the System Administrator security role. When agent creation and management are scoped to security groups, that application user cannot be created until the Capsule application is a member of one of the groups.
- Setup fails for every environment, or for a subset of them, even though the authorizing user is a Global Administrator and a System Administrator in the environment
- Adding the Capsule application manually in the Power Platform admin center (Environments → your environment → Settings → Users + permissions → Application users → New app user) fails the same way: the business unit list does not load, or the panel reports that the user is not a member of the organization
Each environment is provisioned independently, so a restriction that covers only some environments produces a partial install.
In the Microsoft 365 admin center, go to Teams & groups → Active teams & groups and create a dedicated security group for Capsule, for example
Capsule Security. Do not reuse a group that drives Copilot Studio licensing or internal cross-charging: Capsule counts as an extra member there and skews those reports.In the Microsoft Entra admin center, add the Capsule enterprise application as a member of the group. The application appears under Enterprise applications once consent has been granted in Step 2 above.
In the Power Platform admin center, go to Manage → Tenant settings → Copilot Studio authors and add the group.
Review any other Copilot Studio settings your tenant scopes to the same security groups, such as those controlling who can manage or publish agents, and add the Capsule group to each of them.
Return to the Capsule portal, open Integrations, open the row menu of your Power Platform integration, and choose Refresh environments. Confirm that every environment you expect to monitor completes.
Note: Environment-level security groups (Manage → Environments → Edit → Security group) do not block Capsule. Microsoft lets application users run in any environment secured with a security group without being a member, so no change is needed there.
Capsule could not add its application user to some environments, usually because the admin who connected it is not System Administrator there or has no Power Apps or Dynamics 365 license. Microsoft no longer gives Global, Power Platform, or Dynamics 365 admins that role in every environment automatically (Manage high-privileged admin roles).
- In Integrations, select your Power Platform integration row. One or more environments show Failed in the Sync status column. Select the info icon next to Failed (View sync error) to read the cause:
Capsule's application user is not a member of this Dataverse environment. Add it as an application user in Power Platform admin center. - Refresh environments reports Couldn't refresh environments. Its message contains
Capsule could not be registered in <environment names>.If Capsule could not register any environment, it containsNo Power Platform environment could be registered.
Capsule sets up each environment separately, so only some of them may be affected.
The admin who does the fix needs a Power Apps or Dynamics 365 license. Users with only Office licenses (with the Dataverse plan enabled) "aren't pre-provisioned into environments", so assign a Dynamics 365 or Power Platform license. Without a license, Microsoft limits admins to configuring and customizing the system, even with the System Administrator role, which can stop Capsule from adding its application user.
In the Microsoft 365 admin center, go to Users → Active users, select the admin, open Licenses and apps, choose a license, and select Save changes. Microsoft's license guide has the full steps.
Microsoft then syncs the license to each environment, so allow time for it.
If no admin in your organization has a Power Apps or Dynamics 365 license, contact Capsule support.
Do this in each affected environment, signed in as the licensed admin who will finish the fix.
Note: Global, Power Platform, and Dynamics 365 admins can grant themselves System Administrator, but only with the admin role assigned directly, not through a group. Dynamics 365 admins must also be members of the environment's security group, if it has one. If your admin role is activated through Privileged Identity Management (PIM), finish these steps before the activation expires. Microsoft logs each elevation in Purview.
One environment, in the admin center
Sign in to the Power Platform admin center, go to Manage → Environments, and select the environment.
In the command bar, select Membership.
In the System Administrators pane, select Add me.
Many environments, with the Power Platform CLI
Install the CLI with Microsoft's install guide (
dotnet tool install --global Microsoft.PowerApps.CLI.Tool, requires .NET), then runpacto confirm it starts.Run
pac auth createand sign in as that admin. Add--deviceCodeif you have no browser. Runpac auth whoto confirm the active profile.Run
pac admin listand copy the Environment Id of each affected environment from the table.Replace the placeholders with those Environment Ids and run:
$environmentIds = @(
  "<environment-id-1>",
  "<environment-id-2>"
)

foreach ($environmentId in $environmentIds) {
  Write-Host "Elevating in $environmentId"
  pac admin self-elevate --environment $environmentId
}
Use this when the licensed account is a Global, Power Platform, or Dynamics 365 admin, or is already System Administrator in every failing environment.
Make that account System Administrator in each failing environment (see above).
In Capsule, open Integrations, open the row menu of your Power Platform integration, choose Reinstall, and sign in with Microsoft using that account. Reinstall and Refresh environments need permission to manage integrations in Capsule, and Reinstall appears only to users who have it. If you don't see it, ask your Capsule admin to grant that permission or to do these steps with you. If Microsoft asks for admin approval, have a Global Administrator approve the request, then choose Reinstall again.
Capsule adds its application user to every environment in the background and starts a sync. Then choose Refresh environments in the row menu. It re-runs setup with your sign-in, starts a sync, and reports any environment that still fails (the messages are listed under Symptoms above). Run it again until it reports no failures, then check Confirm the fix. If the same environments are reported every time, see Troubleshooting item 4 and the Note under Confirm the fix.
Use this when a different admin does the work, or the licensed account cannot be elevated. The Capsule application ID is cd96f28b-f3a1-40fa-a982-0df2a8f319e8.
Use an admin who has a Power Apps or Dynamics 365 license and is System Administrator in the environment (see above).
Add the application user with either method.
Admin center
- Go to Manage → Environments, select the environment, then go to Settings → Users + permissions → Application users.
- Select + New app user. In the Create a new app user pane, select + Add an app, search for the application ID, select it, and select Add.
- Select a Business Unit and enter an Email address (a contact address your team monitors). Microsoft's application user guide describes both fields.
- Select the edit icon for security roles, choose System Administrator, and select Save. Select Save again to confirm the role assignment.
- Select Create.
CLI (after the CLI setup above)
Replace the placeholders with the Environment Ids from
pac admin list:$environmentIds = @( "<environment-id-1>", "<environment-id-2>" ) foreach ($environmentId in $environmentIds) { pac admin assign-user ` --environment $environmentId ` --user "cd96f28b-f3a1-40fa-a982-0df2a8f319e8" ` --role "System Administrator" ` --application-user }In Capsule, open Integrations, open the row menu of your Power Platform integration, and choose Sync. You can also select Sync now in the integration drawer toolbar. Sync only covers environments already listed under the integration. If an environment you fixed isn't listed, choose Reinstall instead and sign in with the admin from step 1 (see Option A step 2). Capsule then adds that environment and starts a sync.
Environments created later need the same fix, and Capsule adds them only when you choose Refresh environments or Reinstall. Refresh environments sets up a new environment with the account that last connected Capsule, so it works only when that account is a licensed System Administrator there. Otherwise, use Option A, or Option B and finish with Reinstall as described in its step 3.
In Integrations, select your Power Platform integration row. When the sync finishes, each fixed environment's Sync status changes from Syncing to Synced. No other step is needed.
Note: If you are already a licensed System Administrator in the failing environment, a tenant restriction may be the cause instead. See Tenants That Restrict Copilot Studio with Security Groups.
Capsule ingests data from both Copilot Studio and Power Automate through a unified Power Platform integration. Both services share the same Entra ID app and are discovered automatically from each environment.
During setup, Capsule uses the Microsoft Discovery Service to automatically detect all Power Platform environments accessible by the authorizing user. Each environment is registered with:
| Field | Description |
|---|---|
| Name | The environment's friendly name in Power Platform |
| URL | The Dataverse instance URL |
| Environment Type | Production, Sandbox, or Development - classified from the Microsoft organization type |
All Copilot Studio agents, Power Automate flows, and users within each discovered environment are then synced automatically.
Copilot Studio bots are ingested as Agents in Capsule. Each agent includes:
| Field | Description |
|---|---|
| Name | The copilot name as defined in Copilot Studio |
| Type | Conversational |
| Accessibility | Public, Tenant, or Limited - derived from the bot's authentication mode and access control policy |
| Owner | The platform user who owns the copilot |
Each copilot's components are parsed and categorized:
| Component | Category | Description |
|---|---|---|
| Model Agent | Model | The foundational LLM powering the copilot (e.g., GPT-4o). Includes system instructions. |
| Skills | Tool | Actions and plugins the copilot can invoke, including connector-based tools |
| Knowledge Sources | Data Source | Knowledge bases attached to the copilot (e.g., Dataverse, SharePoint, external websites) |
| File Attachments | Data Source | Uploaded files used as data sources, categorized by MIME type |
| Access Channels | Access Channel | Deployment channels such as Copilot Chat and Microsoft Teams |
| External Triggers | Access Channel | External trigger integrations and their connection types |
| Connected Agents | Connected Agent | Other AI agent plugins linked to the copilot |
Capsule fetches conversation transcripts for each copilot and extracts individual activity events:
| Activity Type | Description |
|---|---|
| Tool Invocation | A tool or action was called during the conversation |
| Error | An error occurred during the session |
| Session Started | A new conversation session was initiated |
| Agent Reasoning | The copilot's internal reasoning trace |
| Data Source Accessed | A knowledge source or file was accessed |
| Channel Accessed | An access channel interaction was recorded |
| User Message | A message sent by the user |
| Agent Message | A response generated by the copilot |
Power Automate workflows are ingested as Flows in Capsule. Only modern automation flows (non-managed) are collected.
| Field | Description |
|---|---|
| Name | The flow name as defined in Power Automate |
| Type | DAG (directed acyclic graph) |
| Status | Active, Inactive, or Draft - mapped from the workflow state code |
| Description | Optional flow description |
Each flow's definition is parsed to extract its individual steps:
| Step Type | Description |
|---|---|
| Input | Trigger steps that start the flow (e.g., scheduled, manual, event-based) |
| Output | Response steps that return data |
| Condition | Branching logic (If, Switch) |
| Loop | Iteration steps (Foreach, Until) |
| Subflow | Nested scopes or child workflow invocations |
| External Call | HTTP requests, API connections, and OpenAPI connector calls |
| LLM | AI Builder model invocations |
| Data Operation | Variable manipulation, data transformation (Compose, Filter, Select, etc.) |
Connections between steps represent the execution graph:
| Connection Type | Description |
|---|---|
| Data | Standard sequential execution |
| Conditional | Branch taken when a condition evaluates to true, or a specific switch case |
| Default | Fallback branch (else / default case) |
| Error | Branch taken when a preceding step fails |
Capsule collects flow run history starting from the 7 days before the integration was connected:
| Field | Description |
|---|---|
| Status | The run outcome (e.g., Succeeded, Failed, Cancelled) |
| Duration | Total run time |
| Trigger Type | What initiated the run |
| Error Code / Message | Error details if the run failed |
Power Platform connectors are captured across both Copilot Studio and Power Automate:
- In Copilot Studio - connector references are extracted from bot component actions. Each skill's connector type is identified from its connection reference (e.g., SharePoint, Outlook, Dataverse).
- In Power Automate - connector references are extracted from the flow definition. Each step that uses an API connection (OpenApiConnection, ApiConnection, Http) captures the connector's API ID, operation ID, and connection name.
Connectors provide visibility into which external services and data sources your AI agents and automation flows are interacting with.
Capsule extends the Power Platform integration to cover Power Apps, providing visibility into canvas and model-driven apps within each discovered environment.
Platform users are collected from each Power Platform environment and deduplicated across Copilot Studio and Power Automate. Each user includes their name, email, and job title from the Dataverse system user record.
Once the integration is configured:
- Initial sync begins automatically
- First sync may take several minutes depending on data volume
- View synced agents in Inventory → Agents
- View conversations in Observability → Filter Activity Type - Session
- To block risky tool calls at runtime, set up Copilot Studio Threat Detection
Register Capsule as the external threat detection provider for your Copilot Studio agents. Before an agent calls a tool, Copilot Studio asks Capsule whether to allow it, and Capsule blocks tool calls that violate your prevention policies.
Every time a Copilot Studio agent is about to invoke a tool, Copilot Studio sends Capsule:
- The tool, its proposed inputs, and the agent's reasoning for choosing it
- The user's latest prompt and recent chat history
- Outputs of the agent's earlier tool calls
- Conversation metadata: the agent, the user, the tenant, and the trigger
Capsule evaluates the call against your prevention policies and answers allow or block. On block, the agent stops and tells the user their message was blocked. On allow, the agent continues with no visible change.
Only agents that use generative orchestration call the threat detection provider. Copilot Studio skips classic agents.
- Complete the integration setup above. Capsule identifies your organization by the Microsoft Entra tenant in each request and looks the agent up in the inventory this integration syncs
- Create at least one Prevention policy in Capsule. Without one, every tool call is allowed
- You need permission to create app registrations in your Microsoft Entra tenant, the Power Platform Administrator role, and your Entra tenant ID
Pick the endpoint that matches your Capsule portal URL:
| Capsule portal URL | Endpoint |
|---|---|
https://portal.us-east1.capsulesecurity.io | https://agentsecurity.us-east1.capsulesecurity.io/v1/webhook |
https://portal.us-west4.capsulesecurity.io | https://agentsecurity.us-west4.capsulesecurity.io/v1/webhook |
https://portal.eu-west4.capsulesecurity.io | https://agentsecurity.eu-west4.capsulesecurity.io/v1/webhook |
Use this exact string, with no trailing slash, both for the Entra app and in Power Platform admin center. Microsoft encodes the endpoint into the app's federated credential, so any difference between the two fails authentication.
Copilot Studio authenticates to Capsule with an Entra app in your tenant that uses a federated identity credential, so there is no client secret to store or rotate. You don't give Capsule the app ID: Capsule accepts tokens issued by your Entra tenant for your Capsule endpoint.
- Open Windows PowerShell 5.1 or later as an administrator, install Create-CopilotWebhookApp from the PowerShell Gallery, and change to the folder it was installed in:
Install-Script -Name Create-CopilotWebhookApp
Set-Location (Get-InstalledScript -Name Create-CopilotWebhookApp).InstalledLocation- Run the script with your tenant ID and your Capsule endpoint:
.\Create-CopilotWebhookApp.ps1 `
  -TenantId "<your-entra-tenant-id>" `
  -Endpoint "https://agentsecurity.us-east1.capsulesecurity.io/v1/webhook" `
  -DisplayName "Capsule Copilot Studio Threat Detection" `
  -FICName "CapsuleThreatDetection"
Add -DryRun to validate the parameters without creating anything.
- Copy the App ID the script prints.
In the Azure portal, go to Microsoft Entra ID → App registrations and select New registration.
Enter a name such as
Capsule Copilot Studio Threat Detection, select Accounts in this organizational directory only (Single tenant), and select Register.Copy the Application (client) ID.
Go to Certificates & secrets → Federated credentials and select Add credential.
Set Federated credential scenario to Other issuer and fill in:
| Field | Value |
|---|---|
| Issuer | https://login.microsoftonline.com/<your-entra-tenant-id>/v2.0 |
| Type | Explicit subject identifier |
| Value | /eid1/c/pub/t/<encoded-tenant-id>/a/m1WPnYRZpEaQKq1Cceg--g/<encoded-endpoint> |
| Name | A descriptive name, such as CapsuleThreatDetection |
- Select Add.
<encoded-endpoint> is your base64url-encoded Capsule endpoint:
| Region | <encoded-endpoint> |
|---|---|
| us-east1 | aHR0cHM6Ly9hZ2VudHNlY3VyaXR5LnVzLWVhc3QxLmNhcHN1bGVzZWN1cml0eS5pby92MS93ZWJob29r |
| us-west4 | aHR0cHM6Ly9hZ2VudHNlY3VyaXR5LnVzLXdlc3Q0LmNhcHN1bGVzZWN1cml0eS5pby92MS93ZWJob29r |
| eu-west4 | aHR0cHM6Ly9hZ2VudHNlY3VyaXR5LmV1LXdlc3Q0LmNhcHN1bGVzZWN1cml0eS5pby92MS93ZWJob29r |
<encoded-tenant-id> is your tenant ID's GUID bytes in base64url, not the encoded text of the ID. Compute it in PowerShell:
$tenantId = [Guid]::Parse("<your-entra-tenant-id>")
[Convert]::ToBase64String($tenantId.ToByteArray()).Replace('+','-').Replace('/','_').TrimEnd('=')In the Power Platform admin center, go to Security → Threat detection and select Additional threat detection. This link opens the pane directly.
Select the environment to protect and select Set up.
Select Allow Copilot Studio to share data with a threat detection partner.
In Azure Entra App ID, enter the app ID of the Entra application.
In Endpoint link, enter your Capsule endpoint.
Under Set error behavior, select Allow the agent to respond.
Important: Keep Set error behavior on Allow the agent to respond. With Block the query, every tool call Capsule doesn't answer within one second is blocked, even when no policy matches. See Failure behavior.
- Select Save.
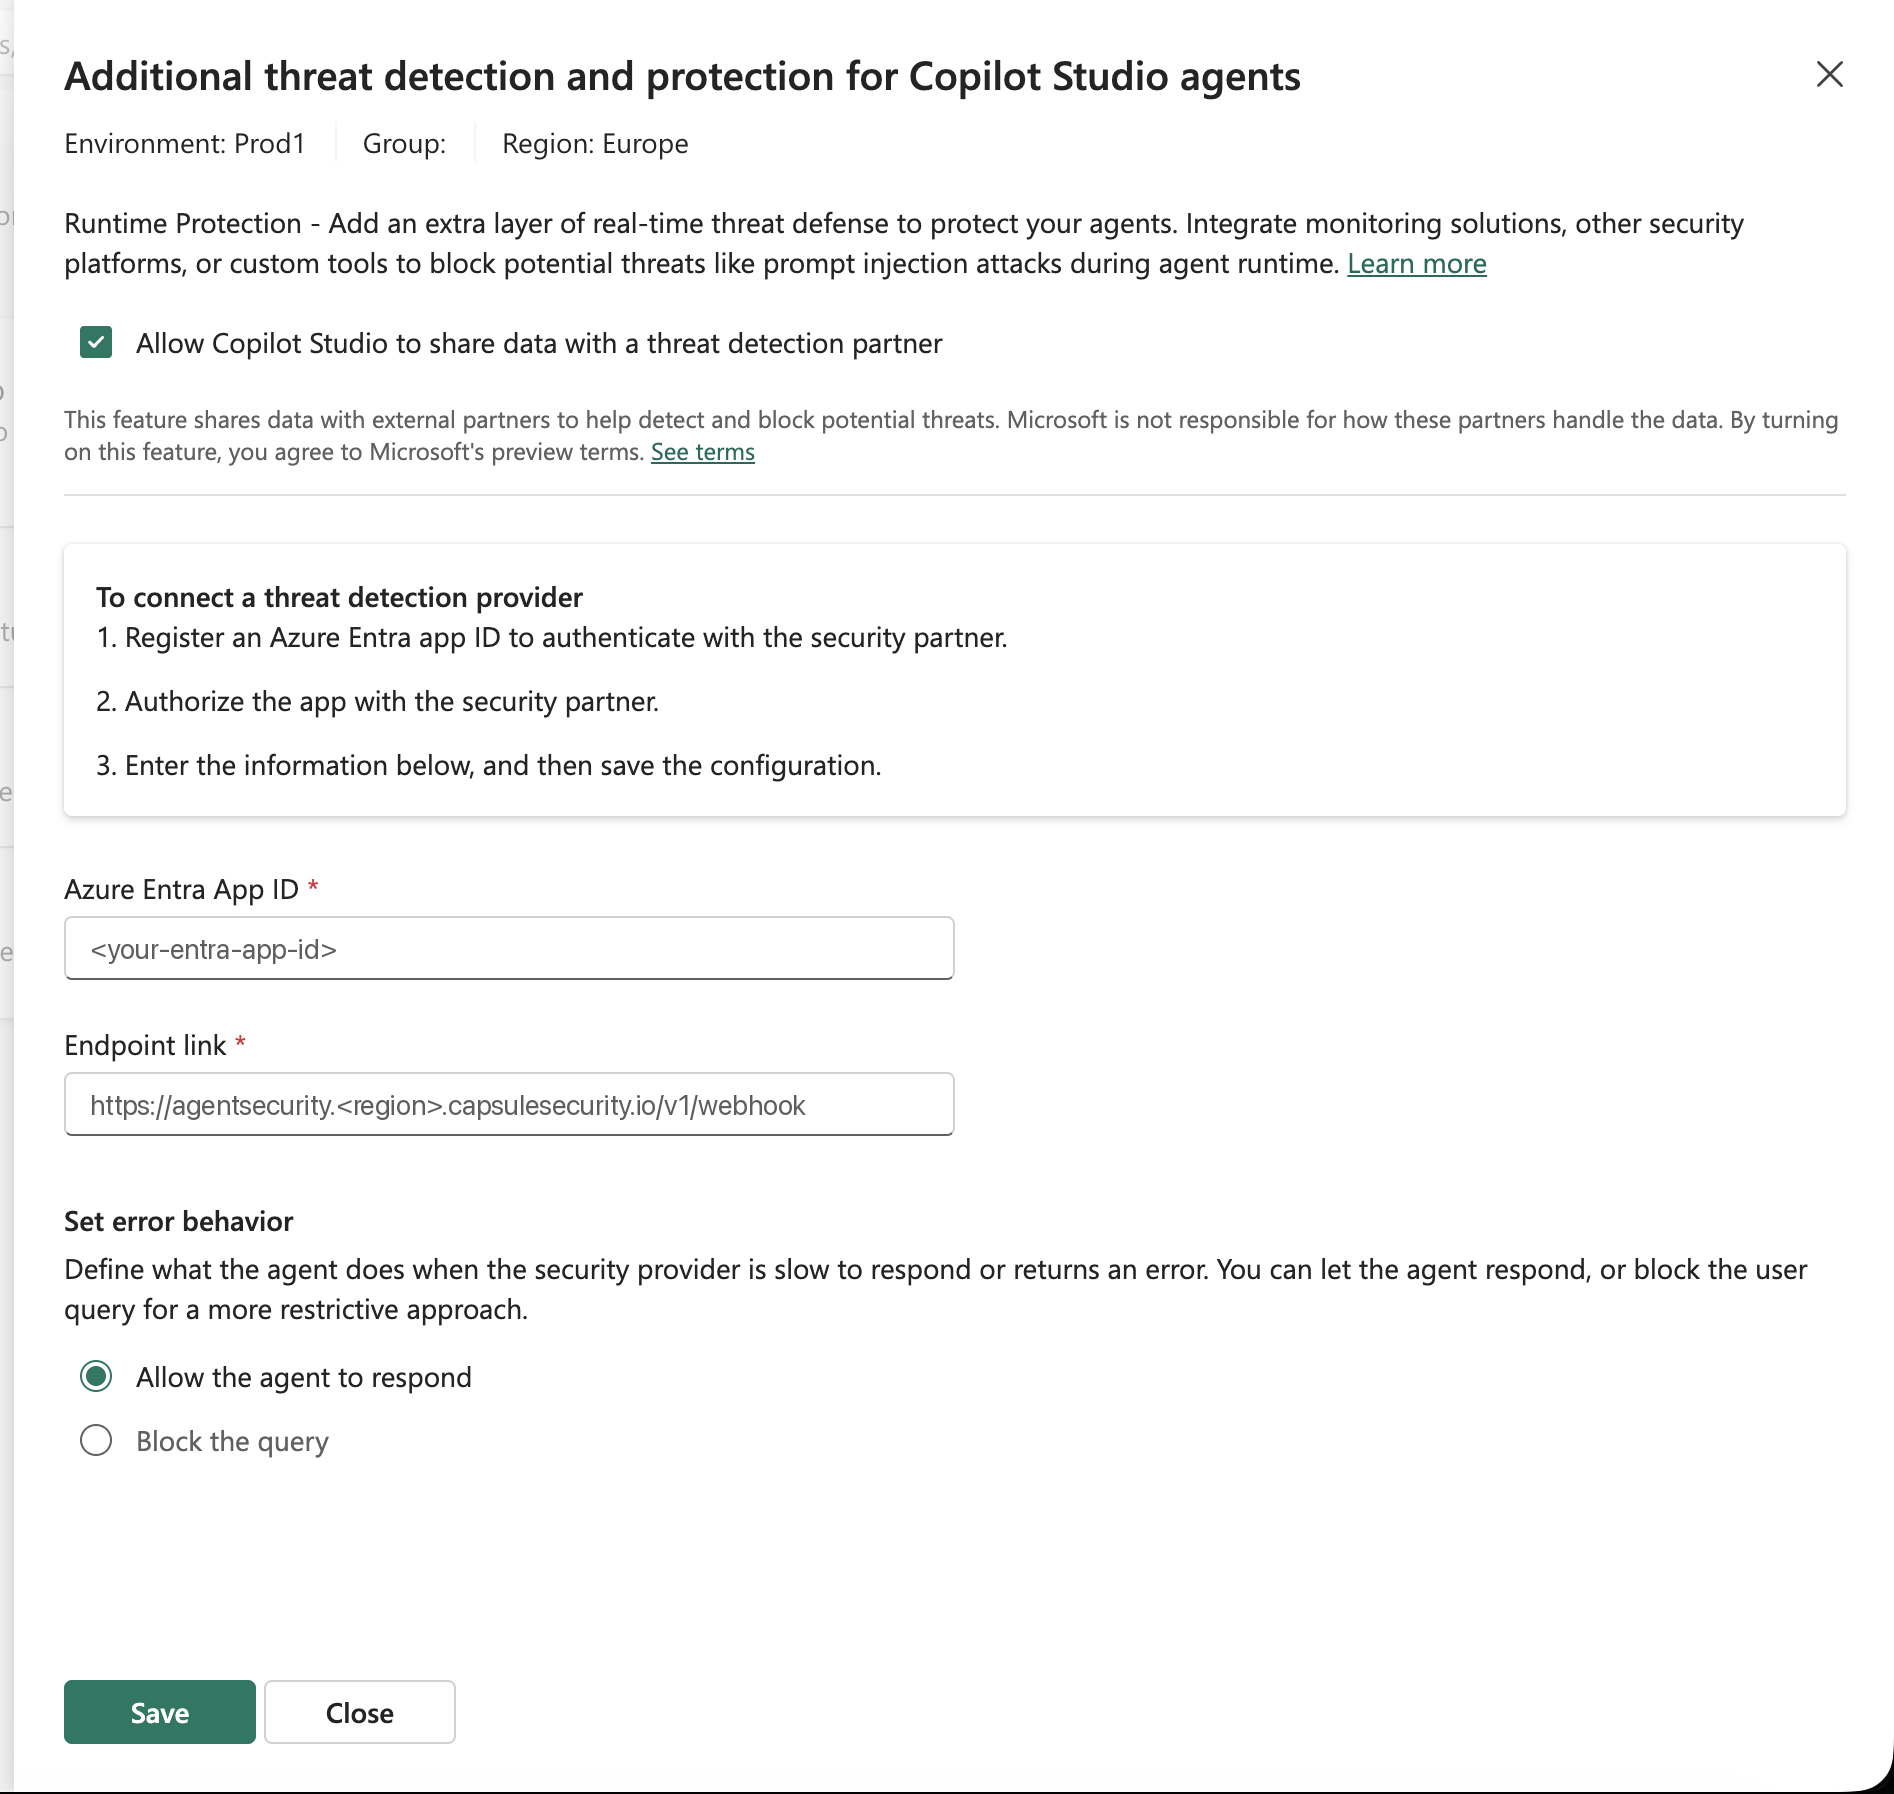
On save, Copilot Studio requests a token with your Entra app and calls Capsule to validate the connection. The save succeeds only if the federated credential and the endpoint match. If it fails, see Threat detection troubleshooting.
Threat detection is set per environment. Repeat this for every environment whose agents you want protected, including environments you create later.
Copilot Studio waits up to one second for Capsule's decision. Set error behavior decides what happens when Capsule times out or returns an error:
| Option | Behavior | Tradeoff |
|---|---|---|
| Allow the agent to respond (default, recommended) | The tool call runs | Availability first - a slow or unreachable Capsule never stops an agent |
| Block the query | The user's message is blocked | Enforcement first - Capsule becomes a hard dependency for every tool call |
Capsule also allows a tool call when it can't match the agent to your inventory, for example an agent created after the last sync. Protection starts once the agent appears in Inventory → Agents.
In Capsule, create a Prevention policy that blocks a tool used by a test agent.
In Copilot Studio, open the test agent in the protected environment and use the Test pane to send a message that makes the agent call that tool.
Confirm the agent stops and replies that the message was blocked.
Delete or disable the test policy.
In the Power Platform admin center, open Additional threat detection, select the environment, and select Set up.
Clear Allow Copilot Studio to share data with a threat detection partner and select Save.
Copilot Studio stops sending tool calls to Capsule for that environment. Inventory and conversation sync continue. Delete the Entra app registration once no environment uses it.
When Save fails, select Copy error info in the admin center to see the underlying error.
| Error | Cause | Resolution |
|---|---|---|
AADSTS700016: application wasn't found in the directory | Wrong Azure Entra App ID, or the app is in another tenant | Copy the app ID again from App registrations |
AADSTS70025: the client has no configured federated identity credentials | The app has no federated credential | Add one as described in Create the Microsoft Entra application |
AADSTS7002111: no matching federated identity record for assertion issuer | Wrong Issuer | Set it to https://login.microsoftonline.com/<your-entra-tenant-id>/v2.0 |
AADSTS7002137: no matching federated identity record for assertion subject | The endpoint in the credential differs from Endpoint link | The error shows the expected subject. Check the region, the /v1/webhook suffix, a trailing slash, or whitespace, then make both values identical |
| "There was a problem connecting to the protection provider" | Copilot Studio couldn't reach Capsule at Endpoint link | Use the exact endpoint for your region. If it still fails, contact Capsule support |
| Symptom | Cause | Resolution |
|---|---|---|
| Tool calls are never blocked | No prevention policy matches the agent or tool | Check the policy's scope in Capsule |
| Tool calls are never blocked | The agent uses classic orchestration | Switch the agent to generative orchestration |
| Tool calls are never blocked | The agent isn't in Capsule's inventory yet | Wait for the next sync, then confirm the agent appears in Inventory → Agents |
| Tool calls are never blocked | The endpoint's region doesn't match your Capsule portal | Recreate the federated credential and Endpoint link with your region's endpoint |
| Users' messages are blocked with no matching policy | Set error behavior is Block the query and Capsule didn't answer within one second | Switch to Allow the agent to respond, or contact Capsule support if timeouts persist |
For Microsoft's side of this setup, see Enable external threat detection and protection for Copilot Studio custom agents.
Consent failed or permissions error
- Verify you are System Administrator in each environment Capsule should monitor. See Prerequisites
- Ensure your account has access to the Power Platform environments
Setup fails for every environment, even as a Global Administrator
- Your tenant likely restricts Copilot Studio to security groups. See Tenants That Restrict Copilot Studio with Security Groups
Some environments show Failed with "Capsule's application user is not a member of this Dataverse environment"
- Capsule could not add its application user there. See Environments Fail with an Application User Error
Environments still show Failed after you made yourself System Administrator
- The admin who connected Capsule may have no Power Apps or Dynamics 365 license. See Before you start: assign a license.
- If an environment still fails after the license is assigned and you are System Administrator there, check your Access Mode:
- In the Power Platform admin center, go to Manage → Environments, select the environment, then go to Settings → Users + permissions → Users and select your user.
- Select ..., choose Manage user in Dynamics 365, and open the Administration tab.
- Under Client Access License (CAL) Information, confirm Access Mode is Read-Write. If it is not, select Read-Write and select Save.
- If Access Mode can't be changed, the license may not have reached that environment yet. Select the user, choose Run diagnostics to sync it, then try again. If it still can't be changed, contact Capsule support.
No environments discovered
- Confirm Copilot Studio or Power Automate resources exist in your environments
- Check that you have the necessary permissions to access these resources
Sync not completing
- Allow several minutes for the initial sync to complete
- Contact support if the issue persists
For help with this integration:
- Email: support@capsule.security
- Include: Your organization ID, integration status, and any error messages
For Power Platform-specific issues: